IP address groups provide centralized management of IP addresses and CIDR blocks and can be referenced by Anti-DDoS and Web protection rules. This helps reduce repetitive configuration and improves the efficiency of policy management.
Note:
IP address groups support cross-site references. An IP address group created for one site can be referenced by protection rules of other sites to maintain consistent protection policies across sites.
When referencing an IP address group in a Web protection rule, you must comply with the relevant restrictions of Match Conditions.
Availability and Quotas
Availability: IP address groups are supported only in the Standard and Enterprise Edition plans.
Quota: The following quota items are tiered by plan. For details, see Plan Comparison.
Number of IP groups per site
Number of IP addresses/CIDRs per site
Number of IP addresses/CIDRs with expiration time in a single group
Note:
The total number of IP addresses/CIDRs in a single IP group is no longer limited separately. It is only constrained by the site-level total number of IP addresses/CIDRs. For IP addresses/CIDRs with automatic expiration configured, quotas are calculated separately by group.
Scenario 1: Managing IP Address Information with Business Threats by Group
Case Scenario
A large game customer has connected sites example.com and site.com. Currently, through the security intelligence library and their own business security, a blocklist of IPs with business threats has been identified. These IP addresses will change dynamically, so they need to be updated in real time and applied to all site domain names, instantly blocking these IPs.
User Guide
1. Log in to the Tencent Cloud EdgeOne console, enter Service Overview in the left menu bar, and click the site to be configured under Website Security Acceleration.
2. On the site detail page, click Security > General Settings.
3. In the IP groups tab, click Edit.
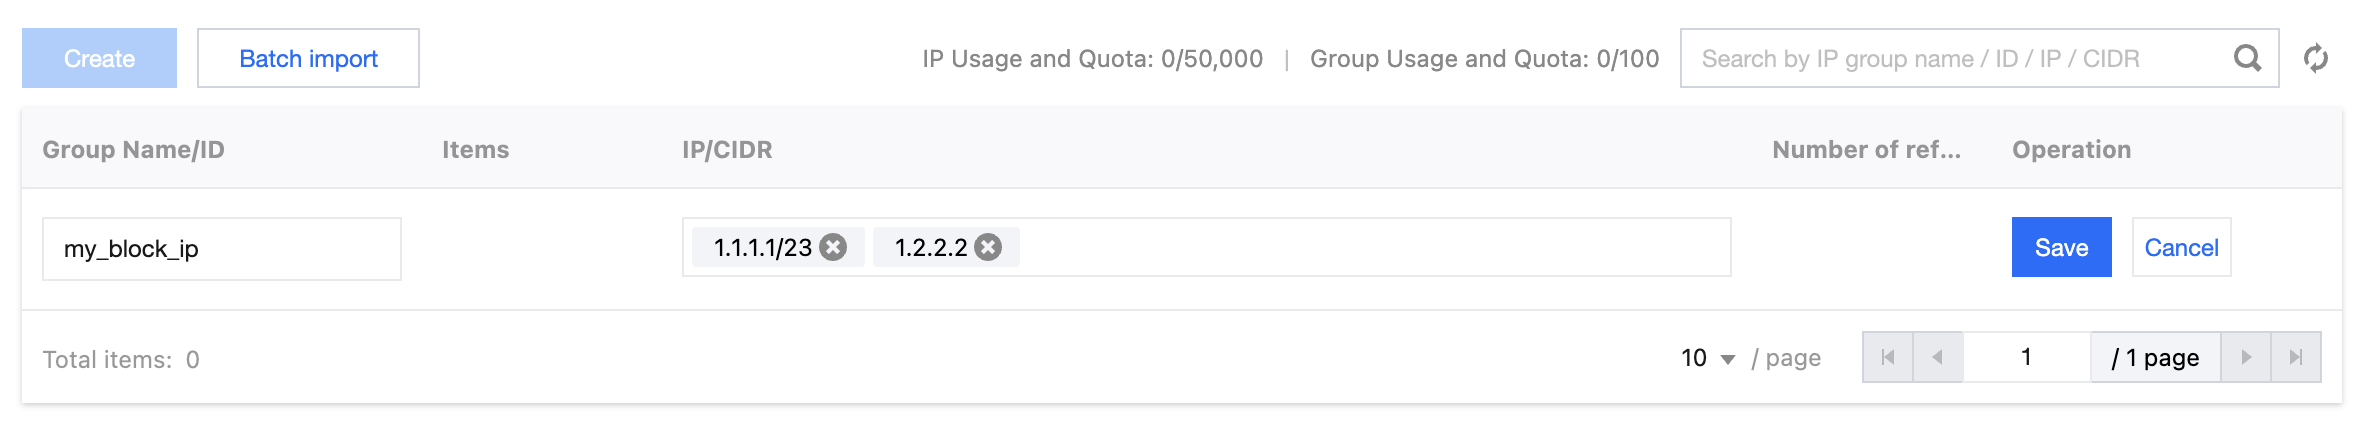
4. Click Create to create a group. Enter the group name and the IP addresses/CIDRs, such as 1.1.1.1/23 and 1.2.2.2. Separate multiple items with carriage returns.
5. Click Save to complete the IP group creation.
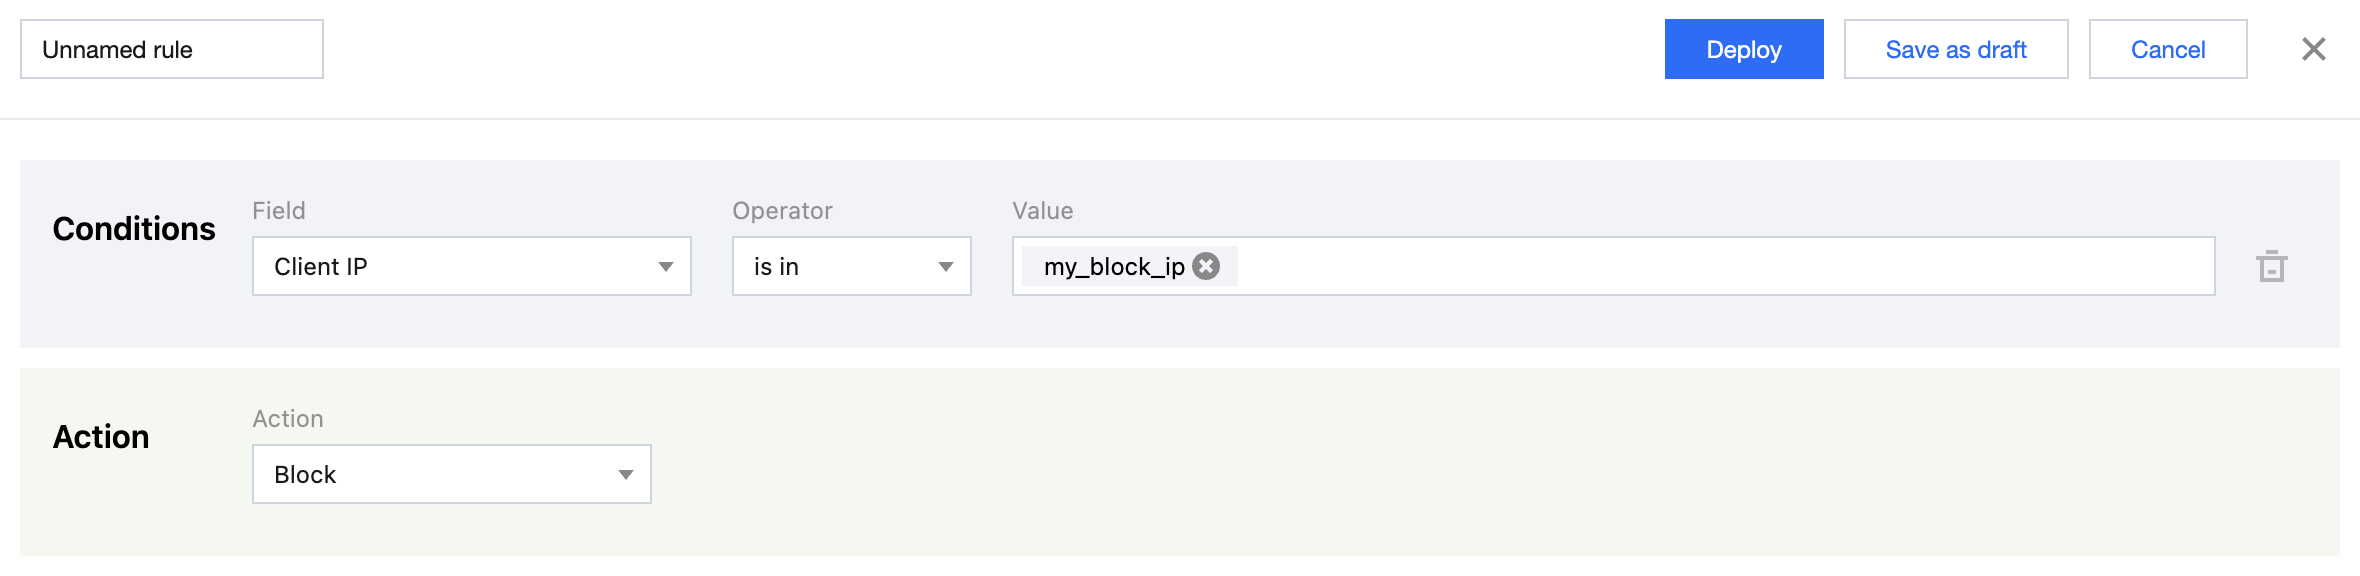
6. After the IP address group is created, you need to block access from all IP addresses in the group. In this scenario, you can add basic access control rules on the Web Security pages of example.com and site.com respectively. When adding a rule, select Client IP equals the group name and set the action to Block. This blocks access from all IP addresses in the group and updates dynamically based on the IP addresses contained in the group. For detailed configuration steps, see Custom Rules.
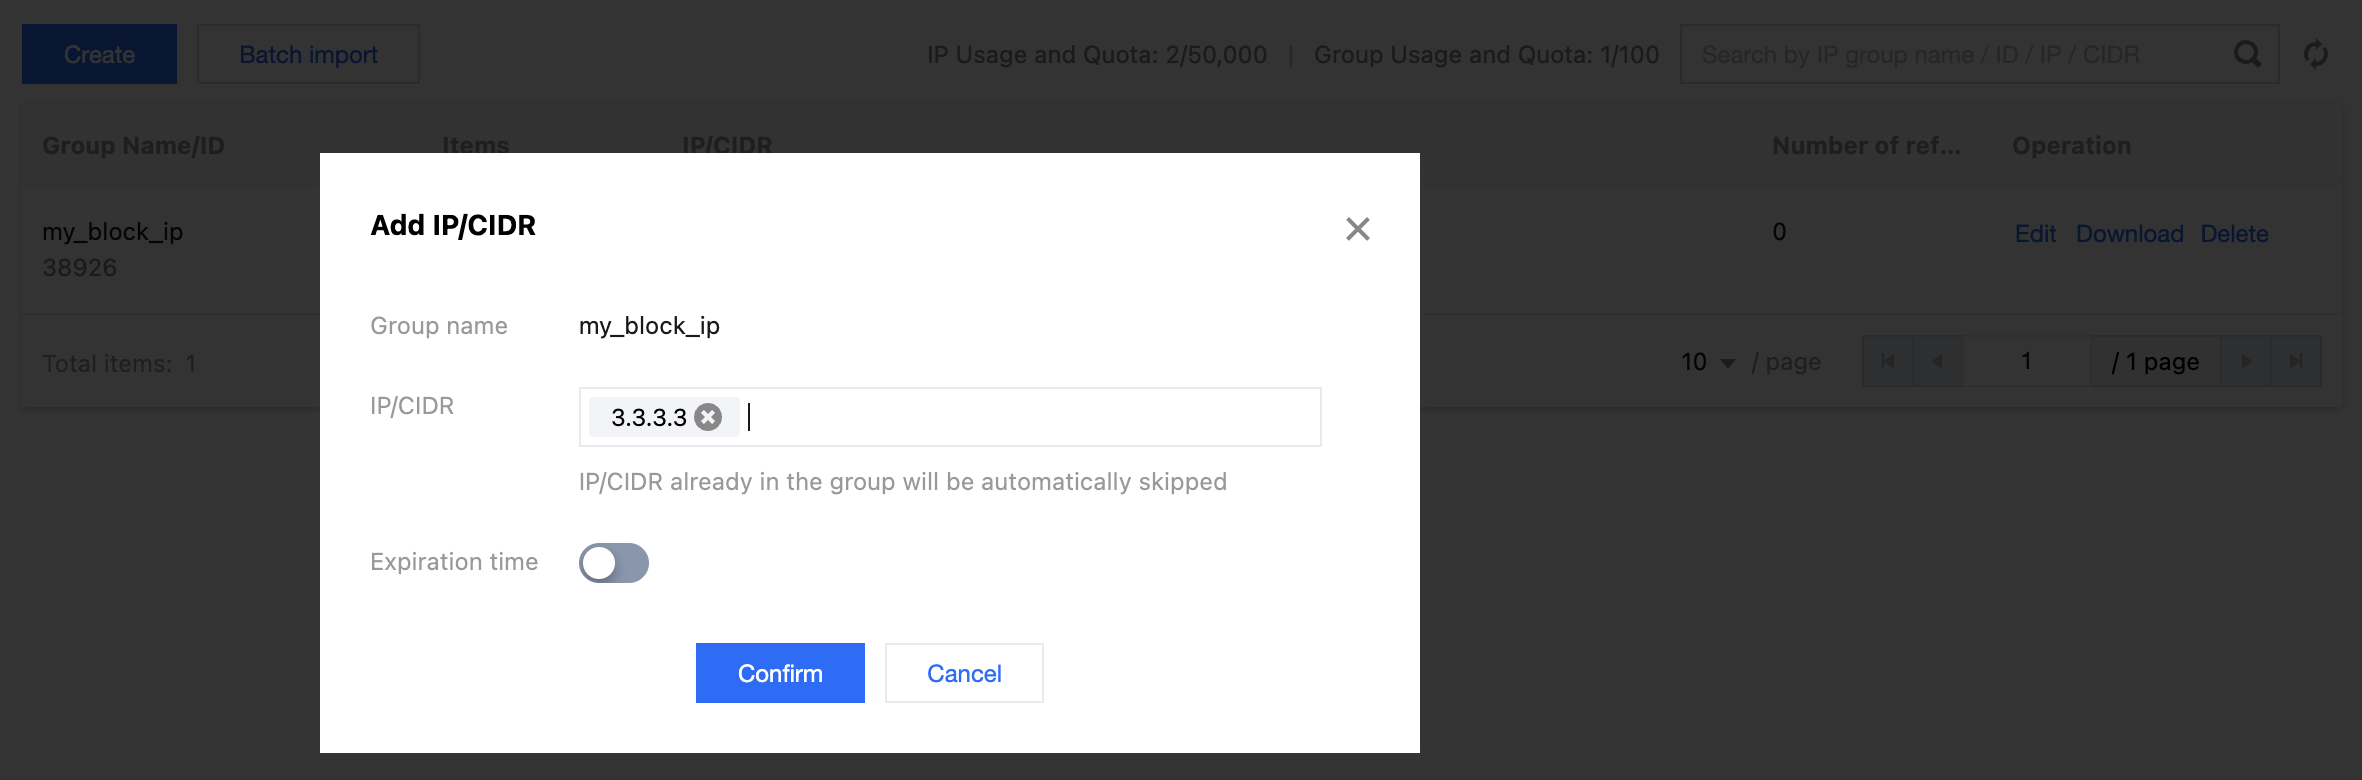
7. (Optional) After configuring the rules, if you identify new risky IPs that need to be added to the group and applied to all sites, you can follow steps 1-3 to re-enter the site where the group was created, click Edit, enter the new IP addresses, and click Confirm to apply the new IP(s) to all protection policies that use this group.
Scenario 2: Adding Auto-Expiring IP Addresses in Batches to an Existing IP Address Group
Case Scenario
An e-commerce customer has configured a long-term valid custom interception rule on the site example.com, referencing the IP group named block_ip to manage blocklist IPs in a unified way. During promotional events, a batch of IPs exhibiting risk behaviors such as malicious crawling and abnormal order placement were identified through monitoring. Since these risks only exist during the activity period, the customer wants to temporarily add these IPs to block_ip and set a unified expiry date, automatically removing them at the end of the activity to avoid long-term blocking of legitimate users, while keeping the existing interception rules in effect without additional maintenance of new protection policies.
User Guide
1. Log in to the EdgeOne console, enter Service Overview in the left menu bar, and click the site that needs to be configured under Website Security Acceleration.
2. Click Security Protection > General Settings to enter the configuration options details page.
3. In the IP group card, locate the target IP group (such as block_ip), then click Edit.
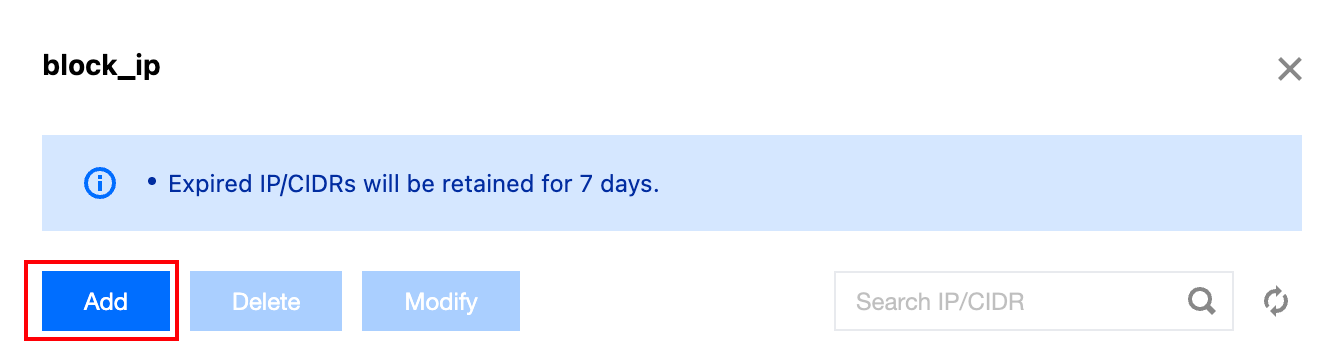
4. In the editing page, click Add.
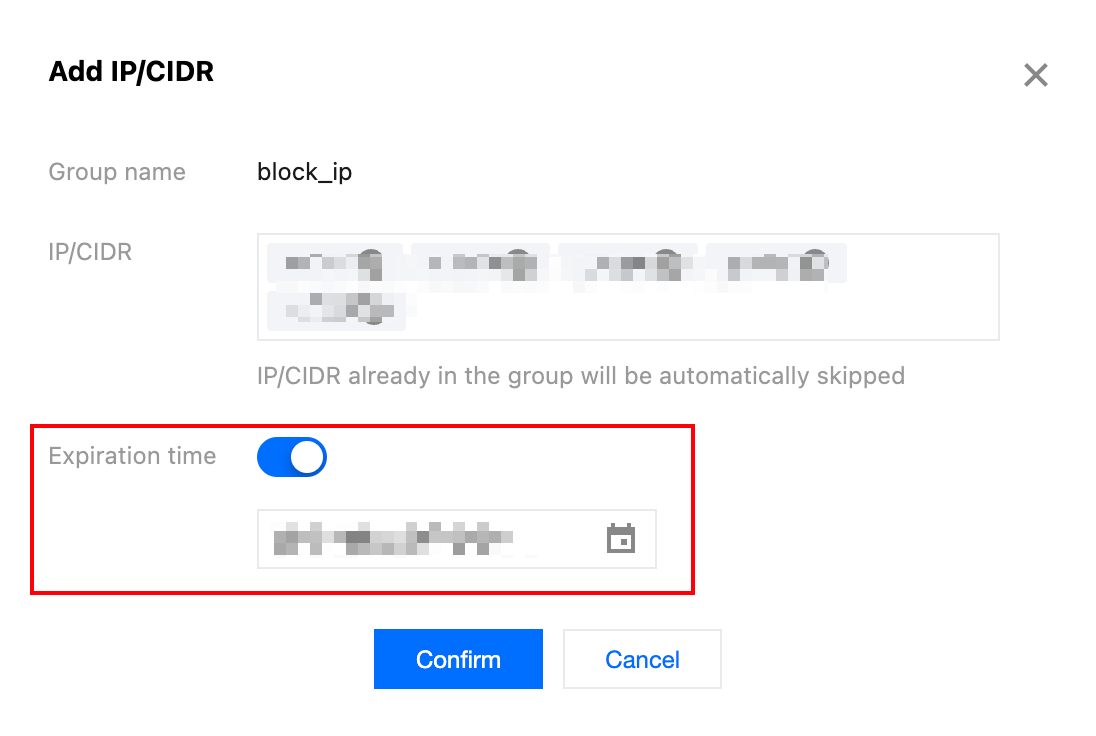
5. In the pop-up window for adding IP addresses or ranges, input the IP address or ranges that need temporary control (bulk entry is supported; multiple addresses are separated by pressing Enter). Check Expiration time and set the expiration time.
6. Click Confirm. Once saved, the temporary control IP will take effect immediately and be automatically removed from block_ip upon expiration.
Scenario 3: Adjusting the Expiration Time of IPs with a Set Expiration Time
Case Scenario
In the block_ip IP address group of the site example.com, a batch of IP addresses identified as sources of abnormal requests are set to expire after 7 days. Subsequent analysis found that the attack behavior is still ongoing, so the expiration time of these IP addresses needs to be extended by 14 days.
User Guide
1. Log in to the EdgeOne console, enter Service Overview in the left menu bar, and click the site that needs to be configured under Website Security Acceleration.
2. Click Security Protection > General Settings to enter the configuration options details page.
3. In the IP group card, locate the target IP group (such as block_ip), then click Edit.
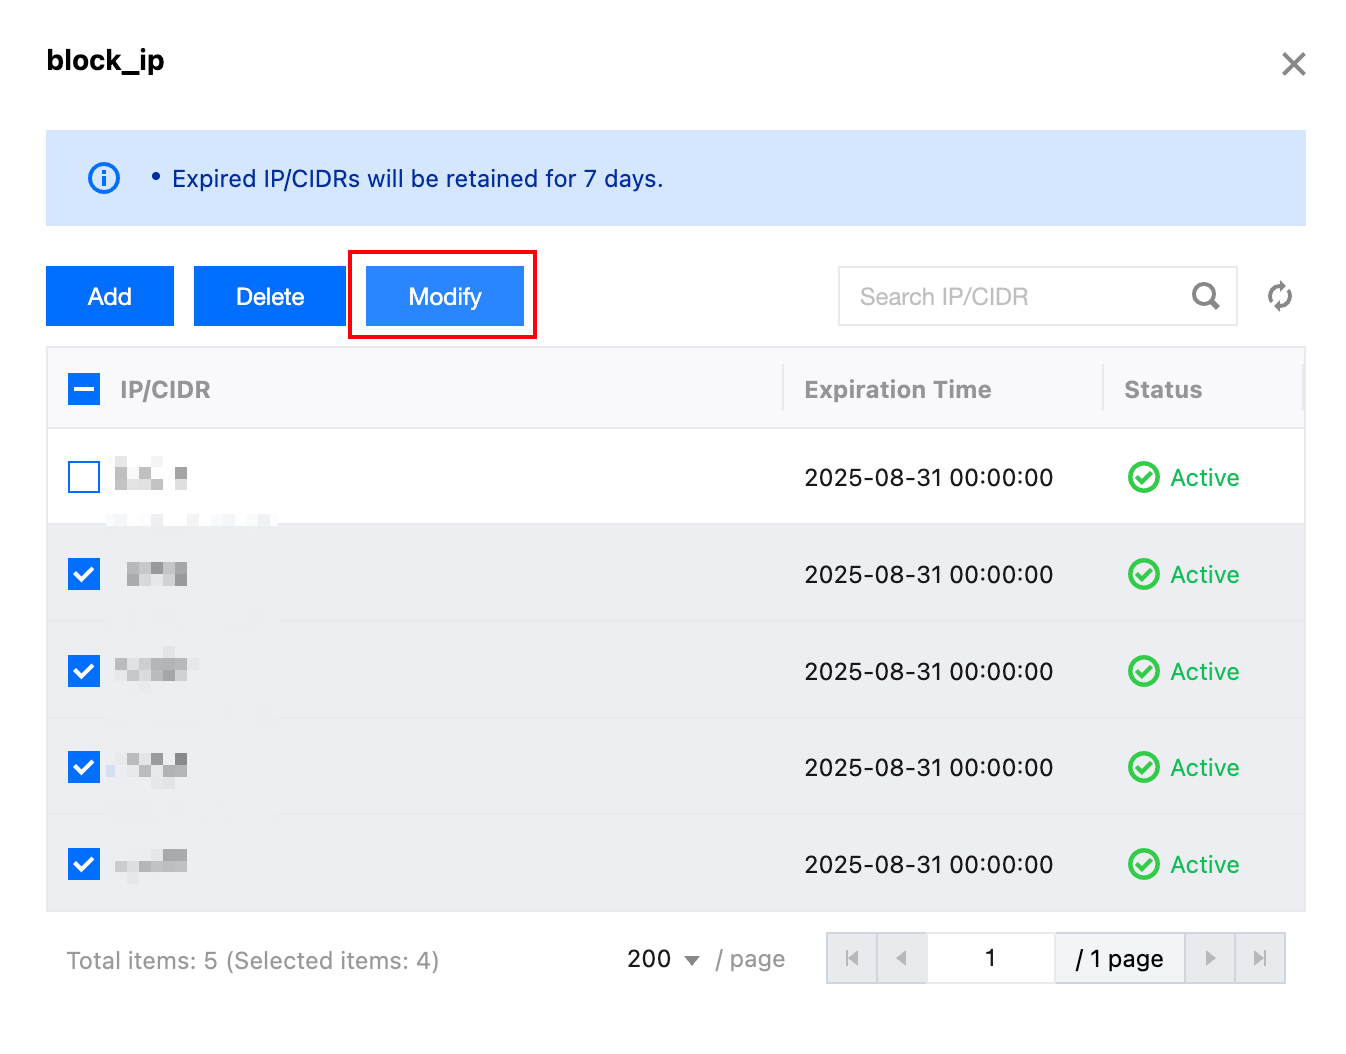
4. On the editing page, select the IP address or ranges that need expiry time adjustment, then click Modify.
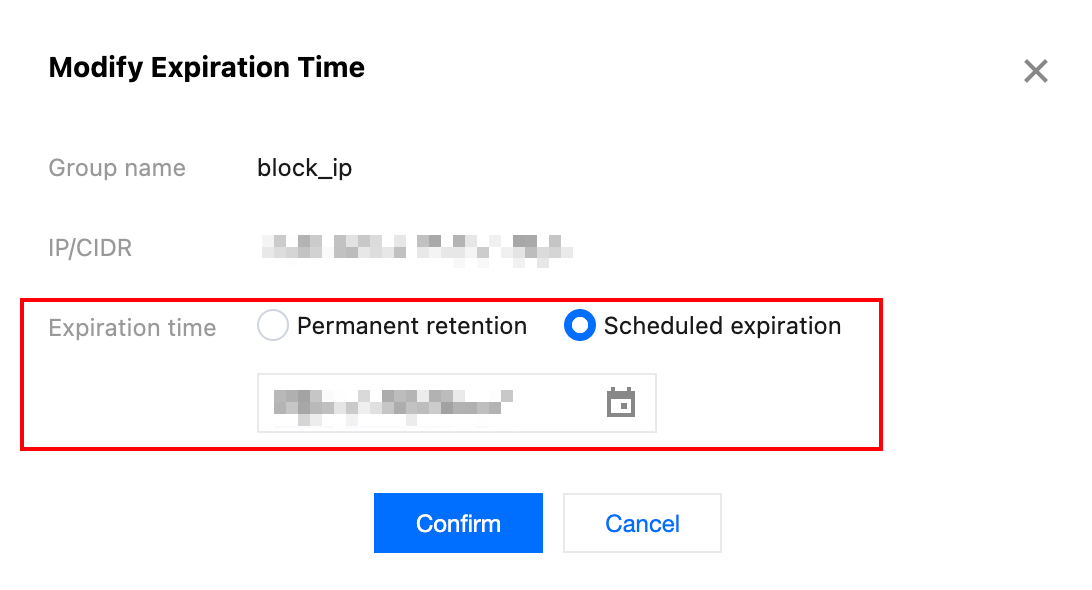
5. In the Modify Expiration Time dialog box, set a new expiration time.
6. Click Confirm. Once saved, these IPs will be automatically removed based on the latest expiry time.