Edge Acceleration
  • Site Acceleration
    • Overview
    • Access Control
      • Token authentication
        • Token Authentication
        • Authentication Method A
        • Authentication Method B
        • Authentication Method C
        • Authentication Method D
        • Authentication Method V
    • Smart Acceleration
    • Cache configuration
      • Overview
      • EdgeOne caching rules introduction
        • Content Cache Rules
        • Cache Key Introduction
        • Vary Feature
      • Cache Configuration
        • Custom Cache Key
        • Node Cache TTL
        • Status Code Cache TTL
        • Browser Cache TTL
        • Offline Caching
        • Cache Prefresh
      • Clear and Preheat Cach
        • Cache Purge
        • URL Pre-Warming
        • Prefetch M3U8
      • How to improve the Cache Hit Rate of EdgeOne
    • File Optimization
      • Content Compression
      • Smart Compression
    • Network Optimization
      • HTTP/2
      • HTTP/3(QUIC)
        • Overview
        • Enable HTTP/3
        • QUIC SDK
          • SDK Overview
          • SDK Download and Integration
          • Sample Code
            • Android
            • iOS
          • API Documentation
            • Android
            • iOS
      • IPv6 Access
      • Maximum Upload Size
      • WebSocket
      • Client IP Geolocation Header
      • Client IP Geographical Location
      • gRPC
      • Network Error Logging
    • URL Rewrite
      • Access URL Redirection
      • Origin-Pull URL Rewrite
    • Modifying Header
      • Modifying HTTP Response Headers
      • Modifying HTTP Request Headers
    • Modify response content
      • HTTP Response
      • Custom Error Page
    • Rules Engine
      • Overview
      • Rule Management
      • variables
      • Supported Matching Types and Actions
    • Image and video processing
      • Audio and Video Pre-pulling
      • Just-in-Time Image Processing
      • Video Just-In-Time Processing
      • VOD Media Origin
    • Speed limit for single connection download
    • Request and Response Actions
      • HTTP Response
      • Processing order
      • Default HTTP Headers of Origin-Pull Requests
      • Default HTTP Response Headers
      • HTTP Restrictions
    • Media Services
      • Audio and Video Pre-pulling
      • Just-in-Time Image Processing
      • Just-in-Time Media Processing
      • VOD Media Origin
  • L4 Proxy
    • Overview
    • Creating an L4 Proxy Instance
    • Modifying an L4 Proxy Instance
    • Disabling or Deleting an L4 Proxy Instance
    • Batch Configuring Forwarding Rules
    • Obtaining Real Client IPs
      • Obtaining Real TCP Client IPs via TOA
      • Obtaining Real Client IPs Through Protocol V1/V2
        • Overview
        • Method 1: Obtaining Real Client IPs Through Nginx
        • Method 2: Parsing Real Client IPs on Application Server
        • Format of Real Client IPs Obtained Through Proxy Protocol V1/V2
      • Transmitting Client Real IP via SPP Protocol
  • Domain name service and origin server configuration
    • Domain Name Services
      • Overview
      • DNS resolution for managed domains
        • Modifying DNS Servers
        • Configuring DNS Records
        • Batch Importing DNS Records
        • Advanced DNS Configuration
      • Access accelerated domains
        • Adding A Domain Name for Acceleration
        • Ownership Verification
        • Modifying CNAME Records
        • Verify Business Access
      • Traffic scheduling
        • Traffic Scheduling Management
    • HTTPS Certificate
      • Overview
      • Edge HTTPS Certificate
        • Overview
        • Deploying/Updating SSL Certificate for A Domain Name
        • Configuring A Free Certificate for A Domain Name
        • Using Keyless Certificate
      • Edge mTLS Authentication
      • Origin Certificate Validation
      • HTTPS configuration
        • Forced HTTPS Access
        • Enabling HSTS
        • SSL/TLS security configuration
          • Configuring SSL/TLS Security
          • TLS Versions and Cipher Suites
        • Enabling OCSP Stapling
      • Related References
        • Using OpenSSL to Generate Self-Signed Certificates
        • Certificate Format Requirements
        • The Difference Between one-way authentication and Mutual authentication
    • Origin Configuration
      • Load Balancing
        • Overview
        • Quickly Create Load Balancers
        • Health Check Policies
        • Viewing the Health Status of Origin Server
        • Related References
          • Load Balancing-Related Concepts
          • Introduction to Request Retry Strategy
      • Origin Group Configuration
      • Origin configuration
        • Origin-Pull Timeout
        • Configuring Origin-Pull HTTPS
        • Host Header Rewrite
        • Controlling Origin-pull Requests
        • Redirect Following During Origin-Pull
        • HTTP/2 Origin-Pull
        • Range GETs
        • Modify Origin
        • Origin-pull Rate Limiting Policy
      • Origin Protection(Obtaining/Updating Origin IP Address Range)
      • Related References
        • ld Version Origin Group Compatible Related Issues

HTTP/2

What is HTTP/2?

EdgeOne supports clients to initiate requests using the HTTP/2 protocol. HTTP/2 (i.e., HTTP 2.0, the second version of the Hypertext Transfer Protocol) is the second major version of the HTTP protocol, which can effectively reduce network latency and improve site page loading speed.

Use Limits

Upload scenario: Due to the default flow control window limit in EdgeOne, large file uploads may experience reduced transmission speeds if the window is exhausted. If you need to upload files larger than 512 KB, it is not recommended to enable HTTP/2.
Download scenario: It is recommended to evaluate the flow control window size declared by the client-side or server-side HTTP/2 implementation. If the client-side window is small (for example, in a mobile weak network environment), enabling HTTP/2 may not achieve the expected acceleration effect. The HTTP/2 flow control window is 512 KB.
Note:
1. If the client request does not use HTTP/2, EdgeOne is compatible with HTTP 1.x protocol access.
2. For configuring access requests, please refer to this document. If you need to configure HTTP/2 to follow the origin, please refer to HTTP/2 origin-pull.
3. Starting from November 23, 2023, for security reasons (for details, see DDoS Protection Against HTTP/2 Protocol Vulnerabilities), HTTP/2 is disabled by default for new sites. Users can enable it as needed.

Prerequisites

All access domains of the current site have been configured with SSL certificates. For instructions on how to configure SSL certificates, see Certificate Configuration.

Directions

Scenario 1: Modify HTTP/2 support for all domain names of the site

If you need to enable or disable HTTP/2 for the whole connected site, please follow the steps below:
1. Log in to the Tencent Cloud EdgeOne console, enter Service Overview in the left menu bar, and click the site to be configured under Website Security Acceleration.
2. On the site details page, click Site Acceleration to enter the global site configuration page. Then click Network Optimization in the right sidebar.
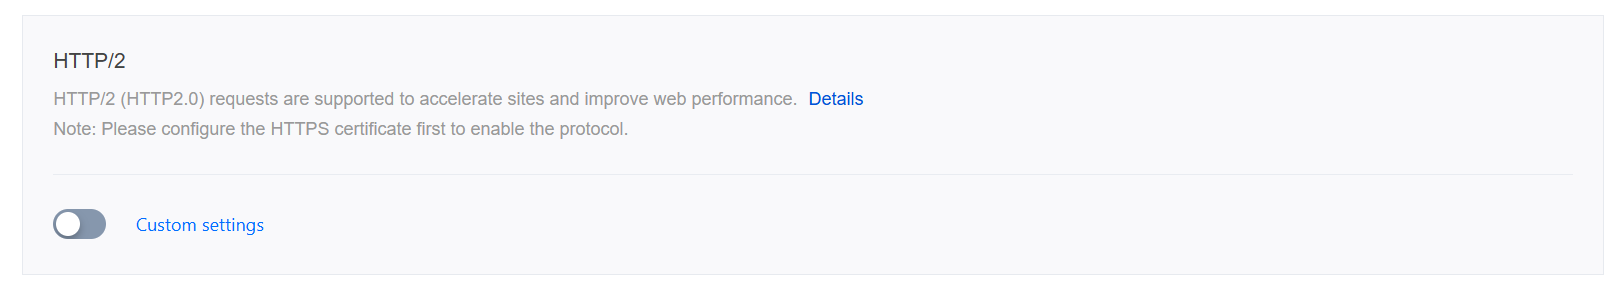
3. Locate the HTTP/2 configuration card. This protocol is disabled by default. Toggle the switch to enable it.


Scenario 2: Enable HTTP/2 for a specified domain name

If you only need to enable or disable HTTP/2 for a specified domain name, please follow the steps below:
1. Log in to the Tencent Cloud EdgeOne console, enter Service Overview in the left menu bar, and click the site to be configured under Website Security Acceleration.
2. On the site details page, click Site Acceleration to enter the global site configuration page. Then click the Rule Engine tab.
3. On the rule engine management page, click Create rule and select Add blank rule.
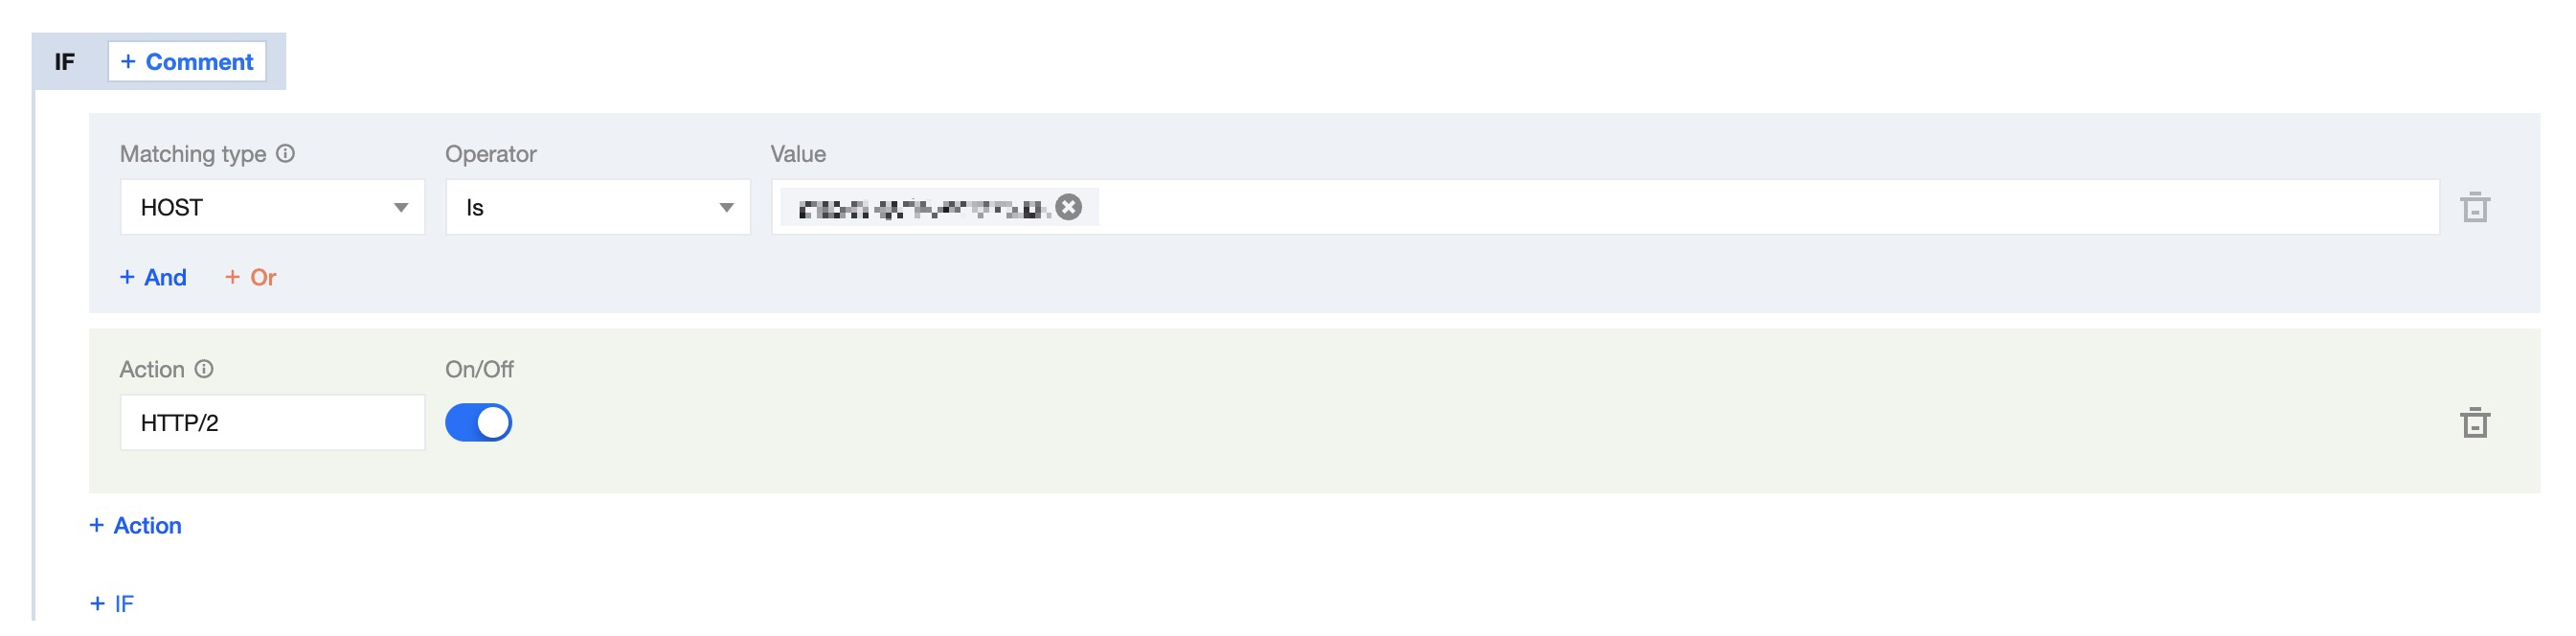
4. On the rule editing page, select the Host matching type to match requests for the specified domain name.
5. Click Action, and in the pop-up operation list, select the operation as HTTP/2. Click the switch to enable/disable.


6. Click Save and Publish to complete the rule configuration.

HTTP/2 Traffic Statistics

The HTTP/2 protocol switch applies to TLS connections rather than individual domain names. Therefore, when multiple domain names share the same connection, you may see H2 traffic from a domain name for which HTTP/2 is not enabled, or H2 traffic concentrated on a single domain name. This is expected behavior for HTTP/2.
The details are as follows:
Prerequisites: Multiple domain names resolve to the same IP address, and the SAN of the same certificate covers these domain names simultaneously.
1. HTTP/2 traffic is counted based on the SNI domain name used when the connection is established. For example, if both domain names A and B have HTTP/2 enabled, and the SNI domain name used when the connection is established is B, then all HTTP/2 traffic on this connection is counted under domain name B.
2. Assume that HTTP/2 is disabled for domain A and enabled for domain B, and the SNI domain used when the connection is established is A. If domain B reuses this connection to send requests, HTTP/2 traffic will also be counted for domain A, which has HTTP/2 disabled.